AI, security and digital trust — built around your workflow, not a demo.
Six sectors, one team. We start with the document queue, the compliance obligation or the control gap that is costing you today, and put AI to work on it with security and DPDP built in from the first sprint.
Which of these describes you?
Every engagement we run begins with one workflow that is measurably slow, exposed or non-compliant. Find yours, then jump to the sector.
Sound familiar?
- KYC packs and loan files arrive as scans and photos; ops re-keys them and credit waits. Financial services
- Discharge summaries and pre-authorisations eat clinician hours, and patient data sits with a dozen vendors. Healthcare
- Grievances and applications pile up faster than officers can categorise them, and dashboards report filings, not resolutions. Government
- Teachers mark late into the evening, and every ed-tech app is collecting children’s data under rules you have not reviewed. Education
- Stock records drift from reality between cycle counts, and the WMS only knows what someone scanned. Logistics
- Procurement reviews and compliance evidence run on email threads, and nobody has an inventory of the AI tools teams already use. Enterprise operations
What every sector engagement shares
- Human-in-the-loop by default: agents draft, extract and rank; your people approve.
- Security testing and DPDP consent design run in sprint one, not after go-live.
- Pilots are scoped for production and measured against your baseline: turnaround, error rate, backlog, exposure.
- Your data stays in your environment. Private AI deployment where regulation or policy requires it.
- Evidence for auditors and regulators is captured as the work happens, in Avisha Trust.
Faster KYC and credit operations, with RBI and DPDP obligations built in.
Loan files, KYC packs and collections notes arrive as scans, PDFs and WhatsApp images. Ops teams re-key them, credit teams wait, and compliance discovers consent gaps after the fact. Meanwhile your mobile app, lending-partner APIs and core-banking interfaces are the attack surface a regulator will ask about first.
- KYC and loan-document intake: extraction, validation against bureau and registry data, exception routing to a human checker
- Fraud and anomaly triage assistants that surface patterns for analysts without making the decision for them
- Retention-vs-erasure policy that reconciles RBI record-keeping with DPDP withdrawal and erasure rights
- VAPT and API security testing for mobile banking, digital lending journeys and partner integrations
- Consent capture and audit trail at onboarding, bureau pull and cross-sell — evidenced in Avisha Trust
- KYC document intake automation pilot on one product line, measured against current turnaround
- DPDP gap assessment for lending and collections journeys
- Application and API security assessment for a customer-facing app
Clinical documentation and patient-data controls that keep pace with the ward.
Discharge summaries, lab reports, insurance pre-authorisations and referral letters consume clinician hours and delay billing. Patient data is spread across HIS, LIS, PACS, insurer portals and app vendors — and under DPDP every one of those is a flow you are accountable for.
- Medical document intelligence: structured extraction from discharge summaries, prescriptions and lab reports, with clinician review
- Intake, pre-authorisation and claims documentation assistants integrated with your HIS
- Patient consent design that covers diagnostics partners, insurers and telemedicine platforms
- Security assessment of hospital information systems, medical-device networks and patient apps
- Breach playbook that includes your lab, pharmacy and app vendors, not only the hospital
- Discharge-summary and claims documentation automation pilot in one department
- DPDP gap assessment for patient-facing apps and diagnostics-partner data sharing
- Hospital information system and clinical network VAPT
Citizen grievance and records intelligence that officers can act on.
Grievance portals, RTI requests, scheme applications and legacy records arrive in volumes no team can read manually. Categorisation is inconsistent, escalations come late, and dashboards report what was filed rather than what remains unresolved. Deployments must run inside government infrastructure and follow public-sector security norms.
- Grievance classification, priority and routing with officer sign-off before any citizen-facing response
- Document automation for applications, certificates and records digitisation, with audit trails
- Governance dashboards that show pending, ageing and repeat issues by ward, district or scheme
- Private AI deployment on department or empanelled cloud infrastructure — no data leaves your control
- Security assessment and data governance for citizen-facing portals and internal systems
- Grievance classification and routing pilot on one portal or helpline
- Legacy records digitisation with searchable extraction for one department
- Security and data-governance review of a citizen services platform
Three sectors in, one of those queues is probably yours — the KYC pack, the discharge summary, the grievance inbox. Bring the slowest one and we will measure it against your current turnaround before anyone proposes a model.
Name the slowest workflowAI-native learning and student-data protection, on one footing.
Teachers spend evenings on marking and question-setting; students get one-size-fits-all practice; leadership sees attendance, not learning. And because most students are children, DPDP applies its strictest rules — parental consent, no tracking, no targeted advertising — to every app and LMS you use.
- Study24by7: AI tutors, adaptive practice, exam preparation and voice-based learning support for students
- Teacher intelligence: question generation, marking assistance and class-level analytics, with the teacher in control
- Institution dashboards for engagement, learning progress and early-intervention lists
- Verifiable parental-consent design and vendor review for LMS, assessment and ed-tech tools
- Security assessment for student information systems and online examination platforms
- Study24by7 pilot for one grade band or programme
- DPDP gap assessment covering children’s data across ed-tech and administrative systems
- Teacher-assist pilot for marking and question generation in one subject
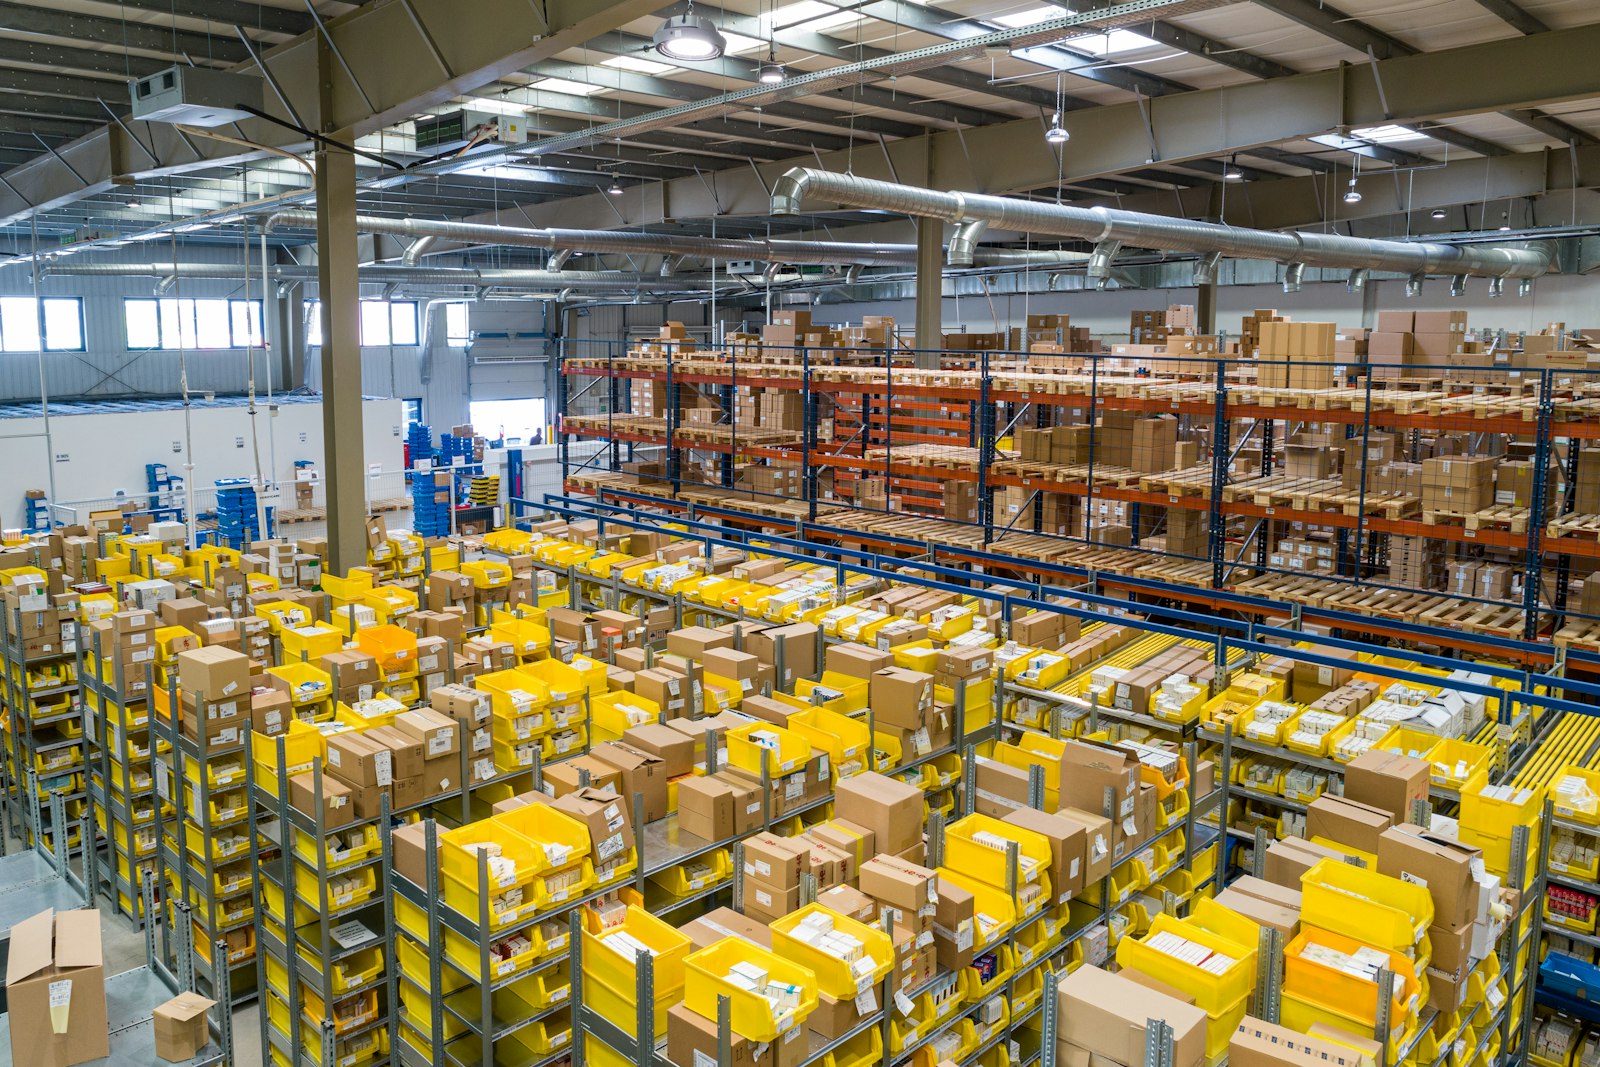
Inventory you can trust without stopping the floor to count it.
Cycle counts pull people off picking. Stock records drift from reality between counts, so promises to customers are made on numbers nobody believes. Quality checks depend on who is on shift, and the WMS only knows what someone remembered to scan.
- RFID-based real-time inventory visibility at dock, rack and dispatch, reconciled against the WMS
- Computer vision for pallet, label and damage checks at receiving and packing
- Automated reconciliation and exception workflows that flag mismatches to a supervisor
- Operations dashboards and alerts: ageing stock, mis-slotting, throughput by shift
- Security review of WMS, IoT and handheld-device networks that now share a LAN with your ERP
- RFID inventory visibility pilot in one warehouse zone, benchmarked against cycle-count accuracy
- Computer-vision receiving and damage-check pilot at one dock
- OT/IoT network and WMS security assessment
Agentic back-office workflows with a human at the sign-off.
Procurement reviews, vendor onboarding, invoice matching and compliance evidence collection run on email threads and spreadsheets. Reviewers become the bottleneck, controls are applied inconsistently, and the audit trail is reconstructed at quarter end. Every new AI tool a team adopts adds an unmanaged data flow.
- Agentic procurement and contract review: clause extraction, policy checks and exception summaries for the approver
- Invoice, PO and vendor-master reconciliation with straight-through processing for clean matches only
- Compliance evidence automation: policy attestations, access reviews and control tests tracked in Avisha Trust
- Enterprise AI governance: model inventory, usage policies, access logs and vendor risk for every AI tool in use
- Managed AI operations: monitoring, evaluation and cost control for agents in production
- Procurement review agent pilot on one spend category, with human approval retained
- AI governance baseline: inventory of AI tools, data flows and vendor risk
- Compliance evidence automation for one framework or internal control set
Point solutions per department, or one team across AI, security and trust.
Point solutions
- An automation vendor, a security vendor and a compliance consultant who have never met
- Pilots chosen because a demo looked good, not because a workflow was measured
- Security and DPDP reviewed after go-live, when changes are expensive
- Nobody owns the model once the integrator leaves
- Evidence for auditors assembled by hand every quarter
With Avisha Global
- One team scopes the workflow, the controls and the consent design together
- Pilot chosen from a measured baseline: turnaround, error rate, backlog, exposure
- Threat model and data map produced in sprint one, not at sign-off
- Managed AI operations keep the model monitored, evaluated and costed
- Avisha Trust captures the evidence as the work happens
One workflow, measured, in production conditions.
The first engagement is deliberately narrow. It proves the method on your documents, your systems and your reviewers before anything scales.
Week 1–2 · Scoping
Pick one workflow. Measure its baseline. Map the data, the systems and the obligations that apply. Agree in writing what “working” means.
Week 3–8 · Pilot in production conditions
Build on your infrastructure with real documents and real reviewers. Security testing and consent design run in parallel, not afterwards.
Week 9 onwards · Scale and operate
Extend to adjacent workflows, hand over runbooks, and move into managed operations with monitoring, evaluation and compliance evidence in Avisha Trust.
Week 1 needs four things from your side: an executive sponsor, a named owner for the workflow, a sample of real documents under NDA, and two workshops. Most clients have that together inside a week.
Set up week 1 scopingWhy sector teams choose one partner for all three.
AI, security and compliance under one team
The people automating your KYC intake are the same people who test the API it runs on and design the consent it depends on. No hand-offs, no gaps between vendors.
Product-backed, not slideware
Avisha Trust runs your compliance evidence and vendor risk; Study24by7 runs learning at scale. We ship and operate software, so pilots are built to be run, not presented.
Built for the Indian regulatory context
RBI, IRDAI, SEBI, CERT-In, DPDP and public-sector procurement norms shape how we scope, host and evidence every deployment — not a template imported from elsewhere.
Human-in-the-loop by default
Agents draft, extract and rank. Your officers, clinicians, analysts and approvers decide. Every pilot ships with review checkpoints and an audit trail.
Frequently asked questions
Don’t see your workflow above?
Tell us the queue that is slowest, the control that is weakest or the audit that is closest. One call is enough to say whether AI, security or trust is the right first move.