DPDP for edtech: most of your users are children. The Act treats that differently.
For founders, product heads, CTOs and compliance leads at learning platforms, test-prep apps, LMS providers and school-management systems. DPDP’s rules for children — verifiable parental consent, no behavioural tracking, no targeted advertising — apply to the core of your product, not the edges. Your school customers are also asking for evidence.
What edtech teams usually discover in week one.
The privacy policy exists. The gaps are operational: what was collected under which consent, who it went to, and whether anyone can prove it. If three or more of these apply, a scoped gap assessment is the right first step.
Sound familiar?
- Students sign up themselves with a date of birth field nobody validates, and parents are never asked.
- Engagement analytics, nudges and streaks are tuned on children’s behaviour with no stated purpose in the notice.
- Ad networks or growth SDKs are embedded in apps used by children.
- Schools hand you student rosters under a one-page order form with no data-processing terms.
- AI tutors store every conversation, including what children say about themselves, indefinitely.
- Parents asking what data you hold on their child are routed to a generic support inbox.
The data a EdTech organisation actually holds.
A DPDP programme starts with an honest inventory. These are the categories we typically find across edtech systems — each needs a purpose, a basis, an owner and a retention period.
- Student identity, class and school
- Learning progress, scores and attempts
- Voice, video and chat with AI tutors
- Parent contact and payment details
- Device and usage data
- Teacher accounts and content
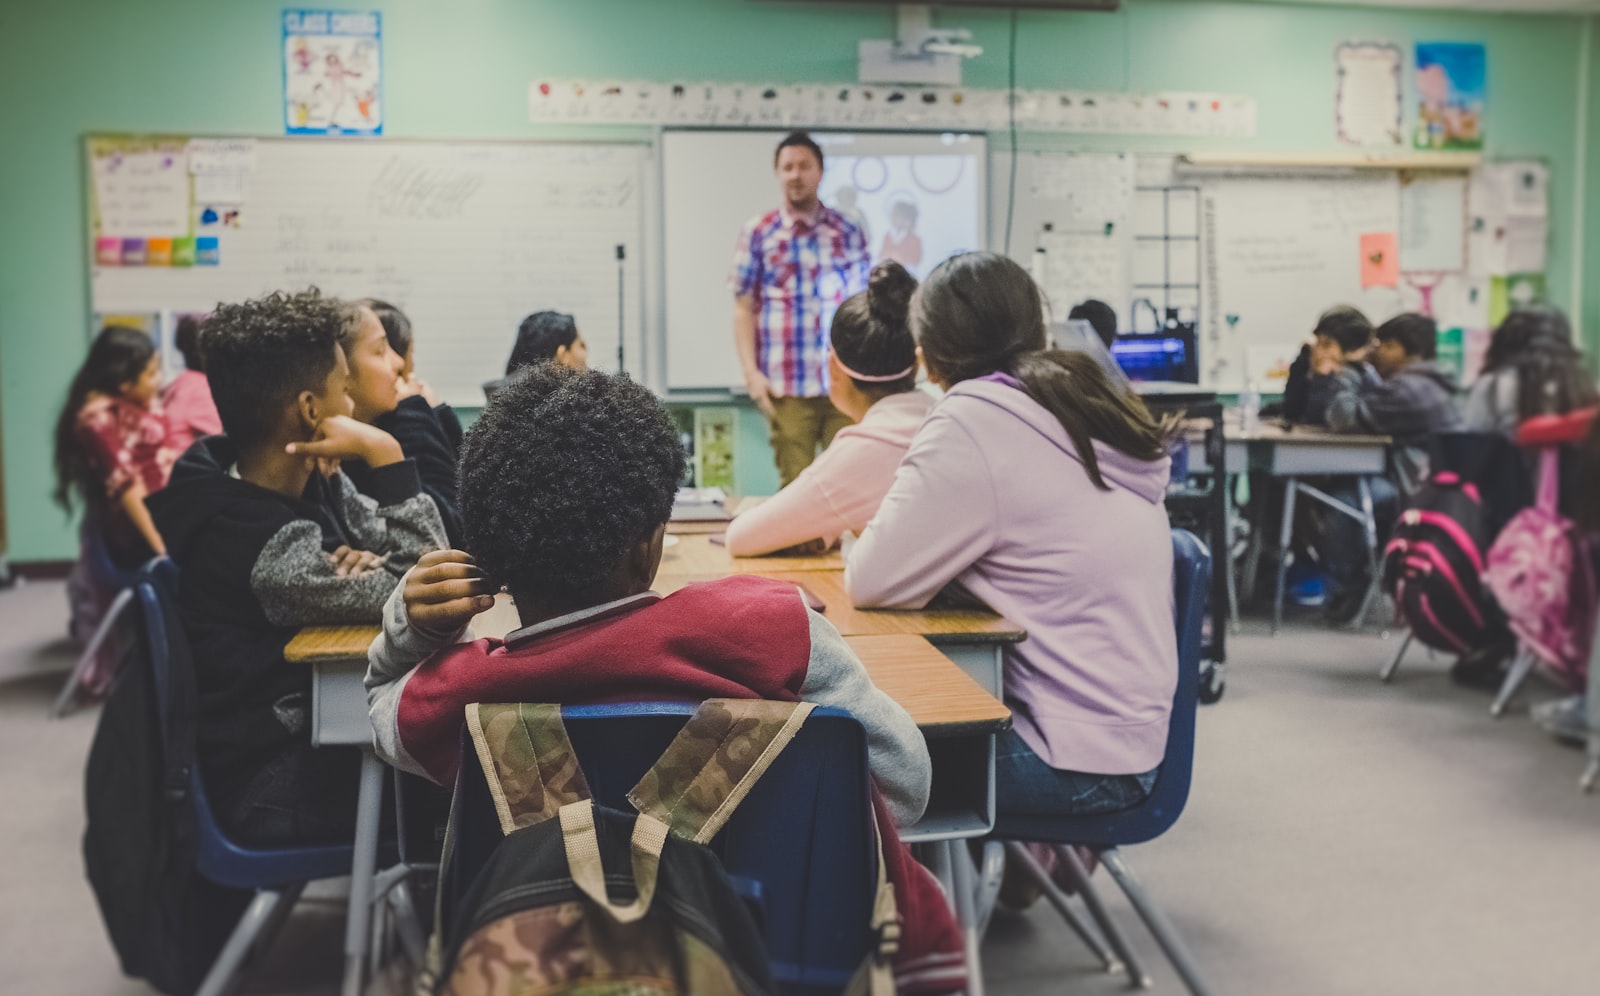
DPDP obligations, translated for EdTech.
The Act is sector-neutral. Its impact is not. These are the obligations that carry the most weight for your workflows.
Verifiable parental consent
Processing a child’s personal data requires verifiable consent from a parent or lawful guardian. Sign-up flows must establish age and obtain that consent before processing begins.
No tracking, behavioural monitoring or targeted advertising directed at children
Engagement optimisation and growth tooling must be reviewed against this rule, not assumed to be “product analytics”.
Notice a parent can understand
What you collect from the child, why, who receives it (school, tutors, vendors), how long you keep it and how to withdraw.
Role clarity with schools
When a school licenses your platform, the school is often the fiduciary and you the processor; direct-to-consumer you are the fiduciary. Contracts and notices must reflect which.
Privacy by design for AI features
AI tutors and voice features collect rich personal data. Minimise, define retention for conversations, exclude children’s data from model training unless clearly consented and safe.
We keep legal specifics general on this page. Section-level analysis, penalty exposure and interpretation are worked through with your counsel during the engagement.
Growth mechanics versus the children’s-data rules.
Most edtech products were built on engagement analytics, personalised nudges and re-marketing. Under DPDP, behavioural monitoring and targeted advertising directed at children are not permitted, and personalisation must be justified as serving the learning purpose. The resolution is a feature-by-feature review, not a policy update.
How we resolve it
- Inventory of every analytics, attribution, ad and messaging SDK, and the data it collects about children.
- Removal or reconfiguration of tracking that does not serve the learning purpose; documented justification for what remains.
- Age and parental-consent gating at sign-up, with consent versioning and easy withdrawal.
- Retention rules for learning data, AI conversations and voice recordings, with deletion on withdrawal or account closure.
Where consent, notice and rights actually show up.
Sign-up & consent
Age determination; verifiable parental consent path; layered notice for parents; consent log versioned against the notice.
Learning & AI tutors
Purpose statements for personalisation; conversation retention limits; training-data exclusion rules; AI systems registered with governance status.
Schools & institutions
Data-processing terms in school contracts; roster handling; role documentation (fiduciary vs processor) per deployment.
Parents & rights
Parent-facing rights portal for access, correction and erasure; withdrawal that stops processing across app, analytics and vendors.
Want to know which of these is your biggest gap? The free assessment takes about ten minutes and scores seven compliance areas.
Run the Gap AssessmentThree ways EdTech clients begin.
Scoped, time-boxed and designed to produce evidence early — so the board and the regulator see progress inside the first month.
First engagements
- SDK and tracking inventory with a children’s-data review of every feature in two weeks
- Parental-consent and age-gating redesign with a versioned consent log
- School data-processing terms and a parent rights workflow evidenced in Avisha Trust
From gap assessment to continuous readiness.
Week 1–2 · Gap assessment
Data inventory, consent and notice review, vendor and rights-process review, breach readiness. Prioritised findings.
Week 3–6 · Remediation sprint
Notice and consent redesign, retention-vs-erasure matrix, vendor contract terms, breach playbook — highest-risk gaps first.
Week 7–12 · Operations
Rights-request workflow, consent logging and evidence store live in Avisha Trust; teams trained; first evidence pack produced.
Ongoing · Monitoring
Quarterly reviews, vendor re-assessment, AI-usage tracking and readiness reporting to the board.
Built for the Indian regulatory stack
We reconcile DPDP with the sector rules that already bind you, instead of importing a foreign template.
Security and compliance from one team
“Reasonable security safeguards” are tested by the people who run VAPT and incident response, not only described in policy.
Evidence, continuously
Avisha Trust captures consent, rights requests and attestations so the answer to “show me” is an export, not a project.
DPDP for EdTech: questions we hear most
DPDP looks different next door.
DPDP for SaaS
DPDP for software companies
DPDP for HealthTech
DPDP for digital health
DPDP for E-Commerce
DPDP for online retail
Start with your sector’s pressure point.
Request a scoped EdTech DPDP assessment, or run the free gap assessment first.